Q. # 1: What is the CompTIA PT0-003 Exam?
The CompTIA PT0-003 Exam, also known as the CompTIA PenTest+ certification, is a comprehensive assessment for cybersecurity professionals focusing on penetration testing and vulnerability management.
Q. # 2: Who is the target audience for the CompTIA PT0-003 Exam?
The CompTIA PT0-003 Exam is designed for cybersecurity professionals, including penetration testers, vulnerability analysts, network security specialists, and security consultants.
Q. # 3: What topics are included in the CompTIA PT0-003 Exam?
The CompTIA PT0-003 Exam covers topics such as planning and scoping penetration tests, gathering information, identifying vulnerabilities, exploiting targets, and reporting and communicating results. Other areas include cloud environments, web applications, wireless networks, and social engineering attacks.
Q. # 4: How many questions are on the CompTIA PT0-003 Exam?
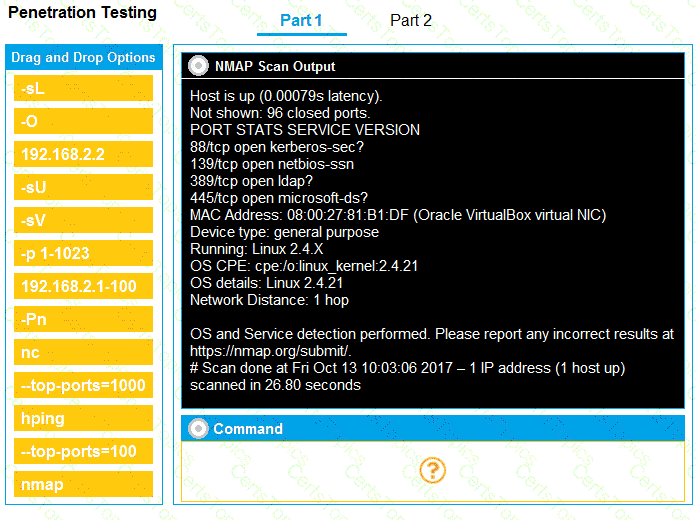
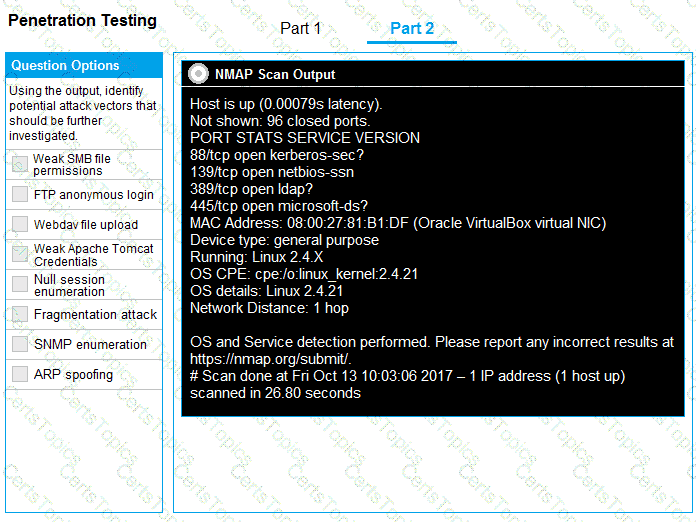
The CompTIA PT0-003 Exam consists of 85 questions, including multiple-choice and performance-based questions.
Q. # 5: What is the passing score for the CompTIA PT0-003 Exam?
A passing score for the CompTIA PT0-003 Exam is 750 on a scale of 100-900.
Q. # 6: What is the difference between CompTIA PT0-003 and PT0-002 Exams?
The CompTIA PT0-003 and PT0-002 exams are both versions of the CompTIA PenTest+ certification, but they have some key differences:
- CompTIA PT0-003 Exam: The CompTIA PT0-003 Exam reflect the latest tools and practices used in penetration testing, including newer technologies that have emerged since PT0-002 was developed.
- CompTIA PT0-002 Exam: The CompTIA PT0-002 Exam focuses more on tools and methodologies that were standard at the time of its release, many of which are still relevant but may not be as comprehensive as the tools covered in PT0-003.
Q. # 7: How can I prepare for the CompTIA PT0-003 Exam?
To prepare for the CompTIA PT0-003 exam, CertsTopics offers high-quality CompTIA PT0-003 exam dumps, questions and answers, and practice tests to help you master the required content. Our CompTIA PT0-003 study guides material are designed to simulate the real exam environment, increasing your chances of success.
Q. # 8: What is the success guarantee at CertsTopics?
CertsTopics offers a success guarantee, meaning that with our CompTIA PT0-003 testing engine and study guides, we are confident that you will pass the exam on your first attempt.
Q. # 9: How often is the CompTIA PT0-003 Exam updated?
The CompTIA PT0-003 exam is updated periodically to reflect changes in technology, security protocols, and best practices in penetration testing. CertsTopics ensures that its PT0-003 exam dumps materials are regularly updated to match the latest exam content.



 India
 Singapore
 French Guiana